Original bilingual journalism · English & తెలుగు
Tata Motors iRA app: CERT-In flags four high-severity flaws, owners told to move to the latest versions
Older builds of the iRA 2.0 and iRA.ev connected-car apps could let an attacker pose as a car owner and reach vehicle data and connected services, the national cyber security agency said. Tata Motors says the fixed versions went out as mandatory updates in August and September.

Owners who use the Tata Motors iRA app to send remote commands to their car, check its health or look up past trips have been asked to make sure they are on the newest version, after the Indian Computer Emergency Response Team (CERT-In) flagged four security flaws in older builds. The national cyber security agency rated the problem High in a note published on Wednesday, 4 November.
The note, CIVN-2026-0537, covers iRA 2.0 up to version 26.7.3, the app for cars with conventional engines, and iRA.ev up to version 26.7.2, the app for electric vehicle owners. CERT-In said the weaknesses could let an attacker obtain sensitive credentials, pose as a user, reach information about the vehicle and its connected features, or alter data held in the app.
Four weak spots in the apps
The first flaw was the most direct. Service account logins, authorisation tokens and API keys sat inside the app package itself, so anyone who downloaded and unpacked it could pull them out and try them against Tata’s backend systems. The second lay in the WebView, the small browser built into the app, which did not properly check the web addresses and origins it opened. Malicious web content pushed to it could be used to capture live login tokens.
The third flaw left authentication tokens in logs meant for development and debugging, where anyone able to read those logs could reuse them to act as the car owner. The fourth was a faulty set-up of SSL certificate pinning, the check that is supposed to stop someone from intercepting traffic between the app and the company’s servers. CERT-In credited researcher Pranav Rajendran with reporting the problems.
What car owners should do
The fix CERT-In lists is a straight upgrade. iRA 2.0 needs build 26.8.2 or later, and iRA.ev needs build 26.9.1 or later; both apps are on Google Play and Apple’s App Store.
Tata Motors Passenger Vehicles responded on Thursday, 5 November, saying the flaws had been handled through software updates and added security measures. According to a company spokesperson, the two versions named by CERT-In were pushed out as compulsory updates during August and September 2026; the app prompts users to install them when it is opened, and the over-the-air update takes a few minutes. Every active user has received it, the spokesperson said, and the company is contacting customers who have not yet switched. Its own assessment found no evidence that customer credentials, personal details or vehicle data had been accessed. CERT-In has logged the four flaws as CVE-2026-121144 to CVE-2026-121147.
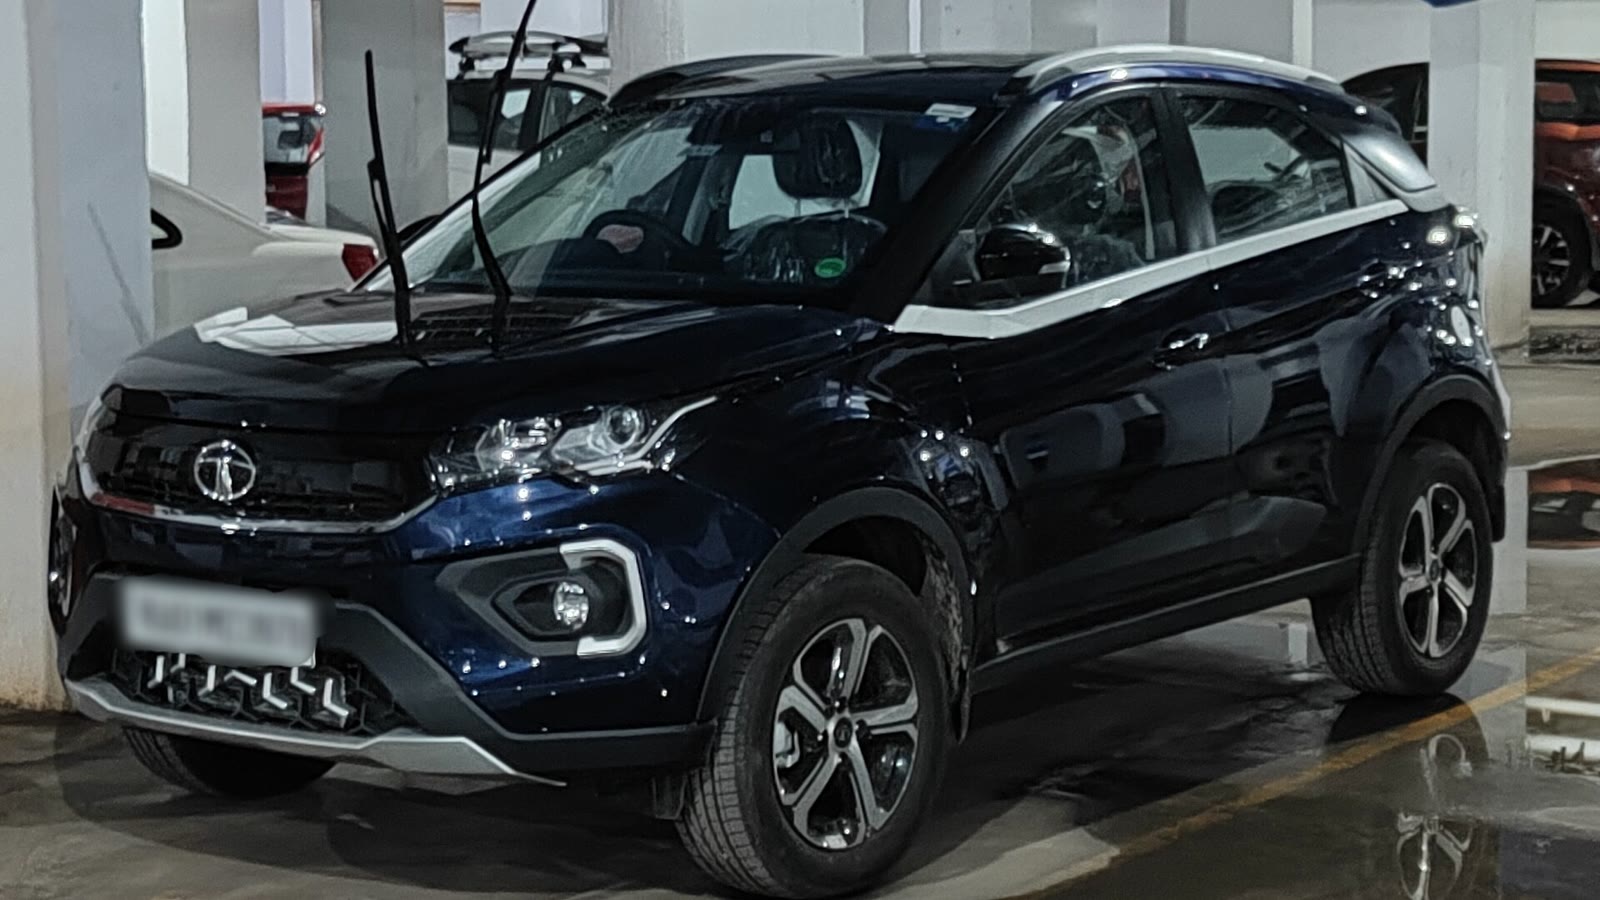
Representative image. Photo: Dairokkan9 / CC BY-SA 4.0 via Wikimedia Commons
More Stories
 TechnologyAadhaar app turns mandatory for property registration in Maharashtra as Nagaland accepts it as ID proof
 TechnologyTRAI’s Network Anubhav maps internet speeds by area and moves DND complaints online
 TechnologyKarbonn Rebel and Rebel Pro: home-grown brand returns to smartphones, Amazon sale from 4 November at Rs 11,999 and Rs 12,499
 BusinessMicrosoft offers a voluntary exit package to 60,000 staff, with India teams on the list
 TechnologyCritical PHP flaws force government websites offline across Europe; update to 8.5.12, 8.4.27, 8.3.36 or 8.2.35
 TechnologySBI finds 3,897 customer records on the dark web and orders an independent probe