Original bilingual journalism · English & తెలుగు
SBI finds 3,897 customer records on the dark web and orders an independent probe
State Bank of India told the stock exchanges on 21 October that names, mobile numbers, dates of birth and addresses in 3,897 customer records had turned up on the dark web. It has brought in an independent cybersecurity agency to investigate.

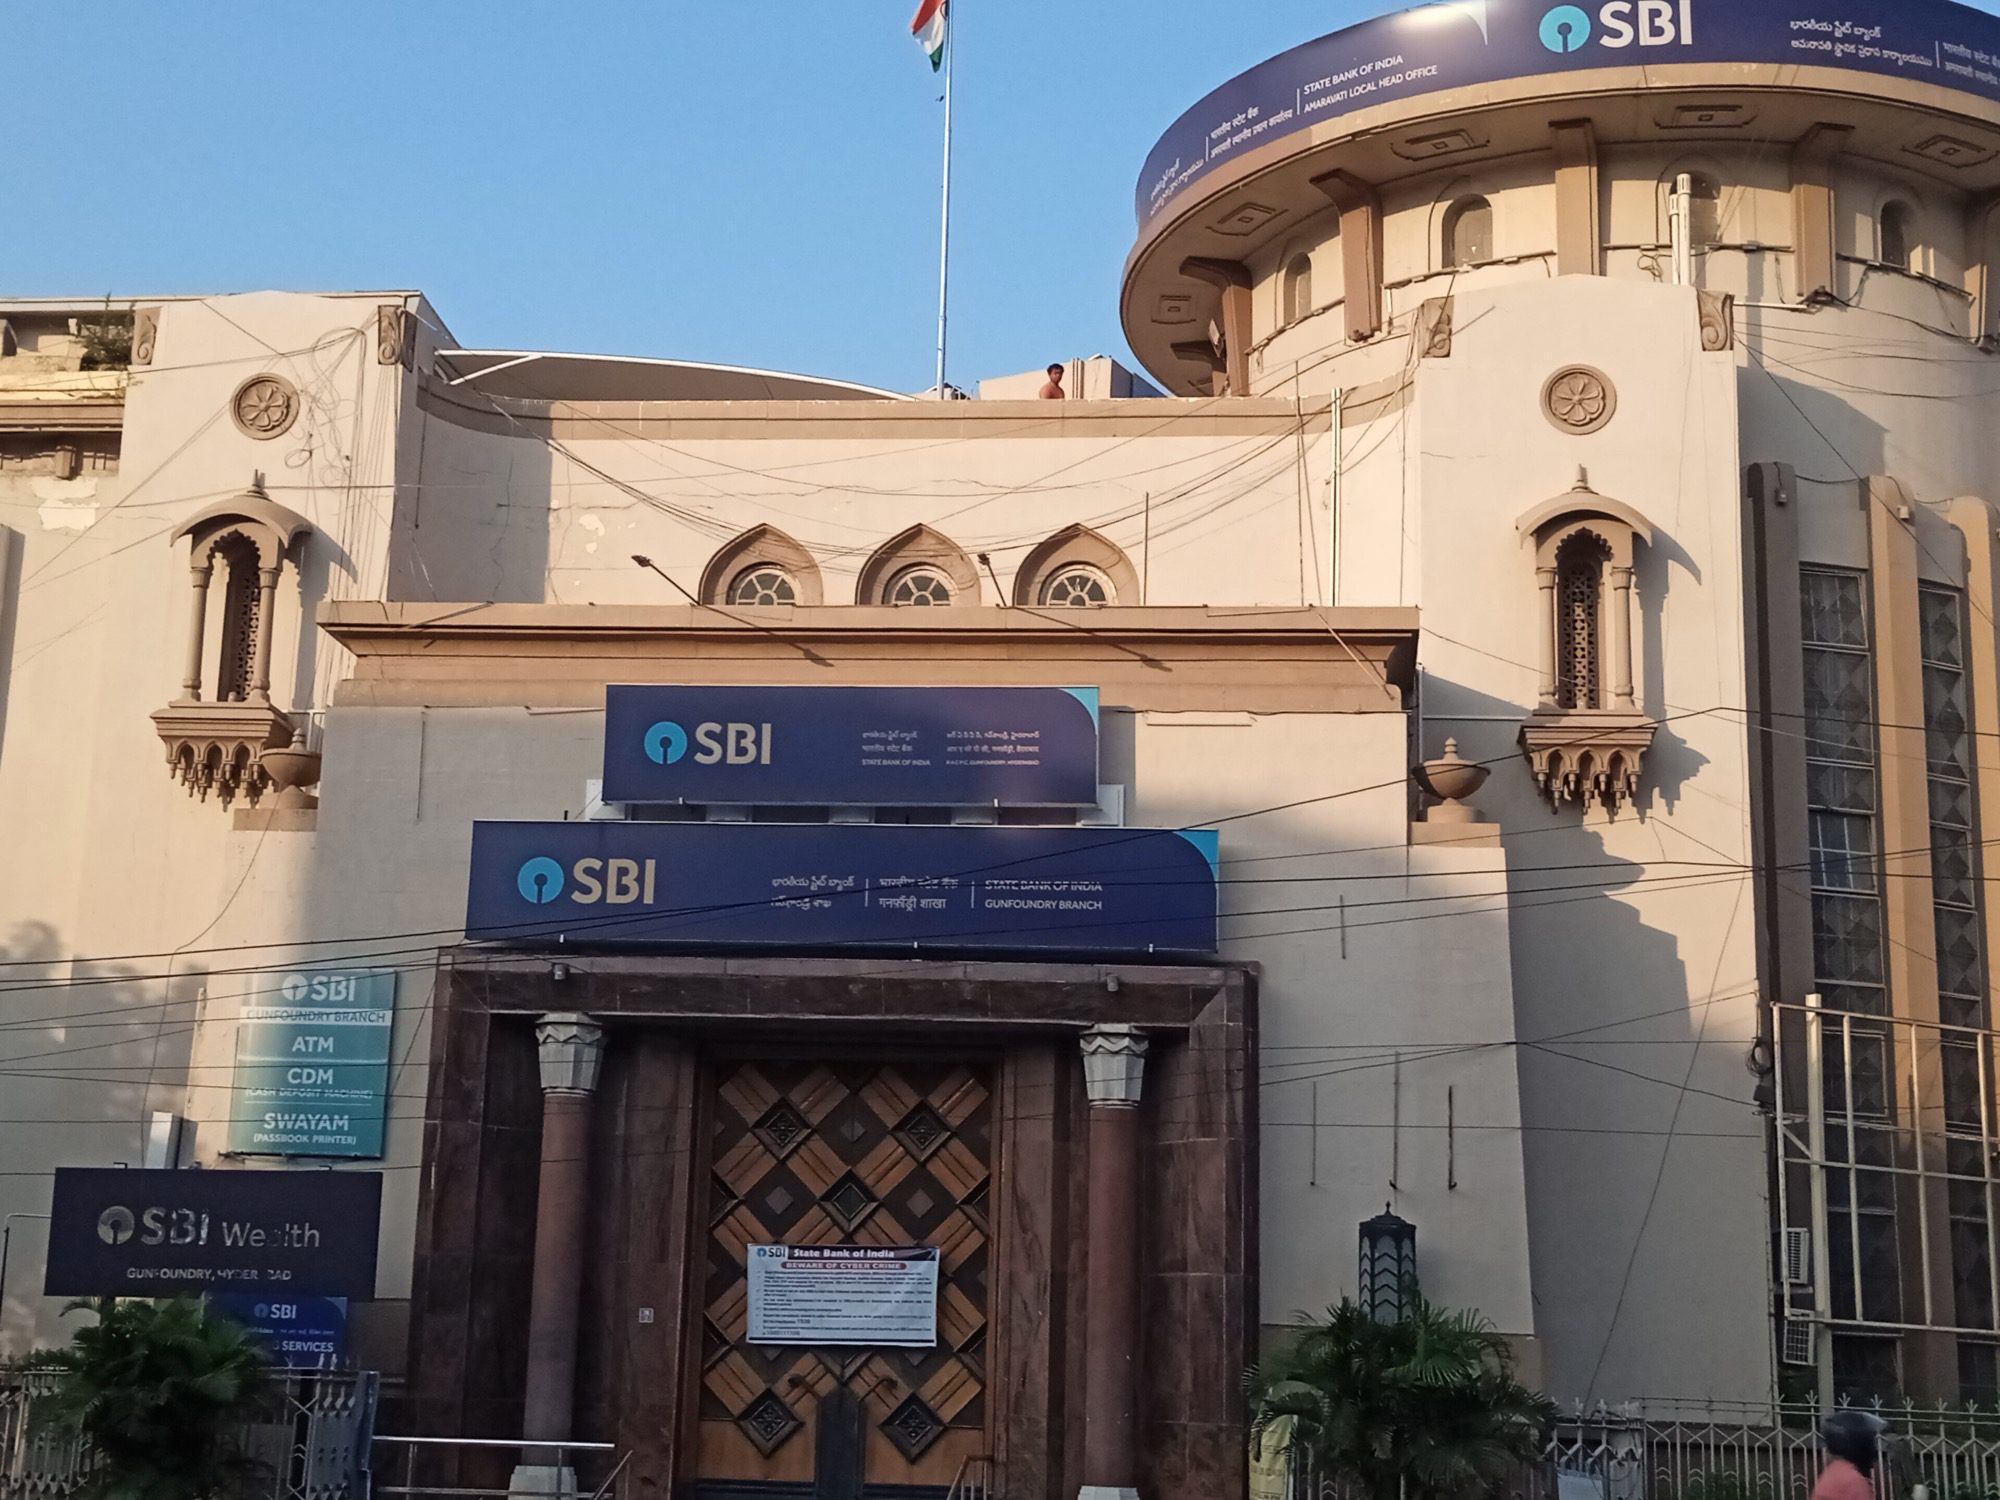
State Bank of India has found personal details of its customers in data available on the dark web and has started an investigation into how they got there. In a disclosure to the stock exchanges on 21 October, the country’s largest bank said a preliminary review of about 3.75 lakh records turned up 3,897 customer records carrying personally identifiable information.
The warning reached the bank on 16 October from three directions: its threat intelligence service provider, the armed forces’ Defence Cyber Agency and CERT-In, the national agency that handles computer security incidents.
What was exposed
According to the filing, the records included customers’ registered mobile numbers, names, dates of birth, gender, email addresses and home addresses. They also carried branch details, customer information file (CIF) identifiers, lead IDs and metadata linked to loan and lead records, along with other related files.
The list in the filing does not mention account balances, card numbers, PINs or passwords. The bank has not yet established where the data came from, or whether it is genuine and complete. It said a detailed investigation was needed to settle those questions and to assess the risks to customers and to the bank.
What the bank has done
SBI said it quickly put its cyber incident response and containment procedures into action. It has engaged an independent cybersecurity agency empanelled by CERT-In to carry out a full assessment of the nature and extent of the compromise, and said remedial and preventive steps are being taken where needed.
The bank told the exchanges that the incident has no material impact on its core business, financial performance or business continuity, and that its core functions are running normally. The filing, made under Regulation 30 of SEBI’s listing rules, does not say whether customers whose details were found will be contacted.
Why customers should stay alert
SBI says it serves more than 50 crore customers. Names, phone numbers, dates of birth and loan-enquiry details are exactly what fraudsters need to make a call or a message sound genuine. Someone who can quote a customer’s name, birth date and branch finds it easier to pose as a bank official offering a loan or asking to “verify” an account.
No customer should share a one-time password, PIN, CVV or internet banking password with anyone who calls, texts or emails, even when the caller gets every personal detail right. It is safer to ignore links in unexpected messages about loans or KYC updates and to reach the bank only through its official website, app or branch. Online fraud can be reported on the national cyber crime helpline, 1930, or at cybercrime.gov.in.
What comes next
The investigation now has to establish whether the leaked material is authentic, where it originated and how wide the exposure is. SBI said it is monitoring the situation closely and will take all steps required under the applicable regulations.
The State Bank of India building at Gunfoundry, Hyderabad, October 2022. File photo. Photo: Adbh266 / CC BY-SA 4.0 via Wikimedia Commons
More Stories
 NationalEurope’s summer heat killed more than 50,000 city residents, a new study finds
 SportsTilak and Nitish turn 112 for 6 into a win: India beat New Zealand by four wickets, lead 2-0
 MoviesPriyadarshi’s Idupu Kayitham to release on 11 December
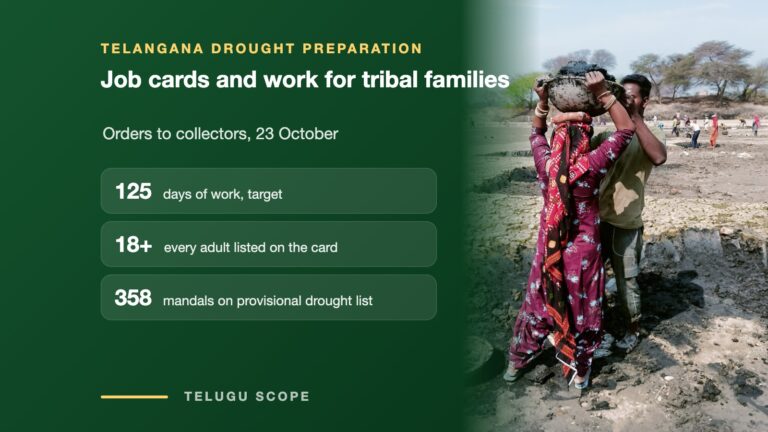 TelanganaTribal families in Telangana to get new job cards and a 125-day work target as drought looms
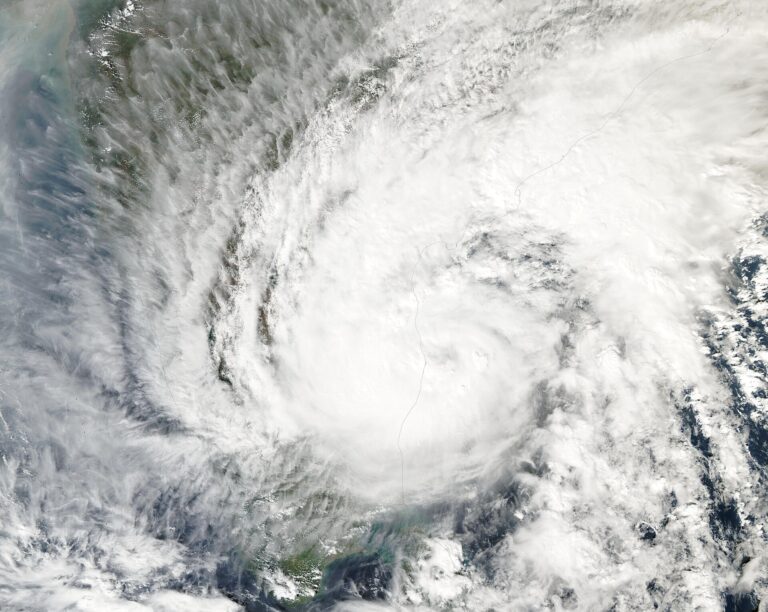 Andhra PradeshBay of Bengal low expected to become a cyclone on 26 October; coastal Andhra braces for heavy rain on 27 and 28 October
 MoviesSalaar 2 shooting begins in June 2027, says Prashanth Neel