Original bilingual journalism · English & తెలుగు
CERT-In warns of Gentlemen ransomware that steals data, then locks files across networks
India's cyber security agency says the gang gets in through exposed VPNs and remote-desktop logins, copies data out, then encrypts Windows, Linux and VMware servers. It advises victims not to pay.

India’s national cyber security agency has asked organisations to close exposed remote-access doors after warning of the Gentlemen ransomware, a criminal operation that copies a victim’s files before locking them. The Indian Computer Emergency Response Team (CERT-In) published the advisory, numbered CIAD-2026-0060, on Friday, 13 November.
CERT-In describes The Gentlemen as a profit-driven gang that rents its malware to other criminals. Victims are squeezed twice: data is taken first, files are encrypted after, and the gang threatens to publish what it stole if no ransom arrives.
How the attack spreads
The way in, the advisory says, is a weak point facing the internet: an unpatched VPN or firewall, a Remote Desktop (RDP) connection, a cPanel hosting login, or a password stolen earlier. Once inside, the attackers map the network using Advanced IP Scanner, Nmap and similar utilities, then misuse Group Policy, the Windows feature that pushes settings to every machine in a domain, to plant their own configuration.
Before encrypting, the malware raises its privileges, stops security and backup services, deletes the shadow copies Windows keeps for restoring files, tries to disable Microsoft Defender and wipes event logs. Stolen data leaves through WinSCP, an ordinary file-transfer program. Written in Go and disguised with a tool called Garble, the ransomware spreads itself from machine to machine and runs on Windows, Linux, BSD, network storage (NAS) drives and VMware ESXi servers.
CERT-In lists manufacturing, healthcare, finance and construction among the sectors hit, and publishes 17 file hashes, seven IP addresses and five web domains linked to the attacks.
Six hours to report
The group has been active for more than a year. Security firm Trend Micro, calling it previously undocumented, detailed its attacks on 9 September 2025: 17 countries hit, manufacturing the worst. On 9 August 2026, Bangladesh’s government cyber response team said victims listed on the gang’s leak site span more than 70 countries. Affiliates, it added, are offered 90 per cent of each ransom.
CERT-In’s checklist starts with exposure: list every service reachable from the internet, shut what is not needed, patch firewalls and VPN appliances, and require multi-factor sign-in on every remote connection. Backups should be encrypted, offline, kept apart from the main network and test-restored regularly. The agency strongly discourages paying, since payment neither guarantees recovery nor stops a leak.
Ransomware is one of the incidents that companies, data centres, service providers and government bodies must report to CERT-In within six hours of noticing, under directions the agency issued on 28 April 2022 under Section 70B of the IT Act, 2000. The rule applies across India, including to companies and government offices in Andhra Pradesh and Telangana. Reports go to incident@cert-in.org.in.
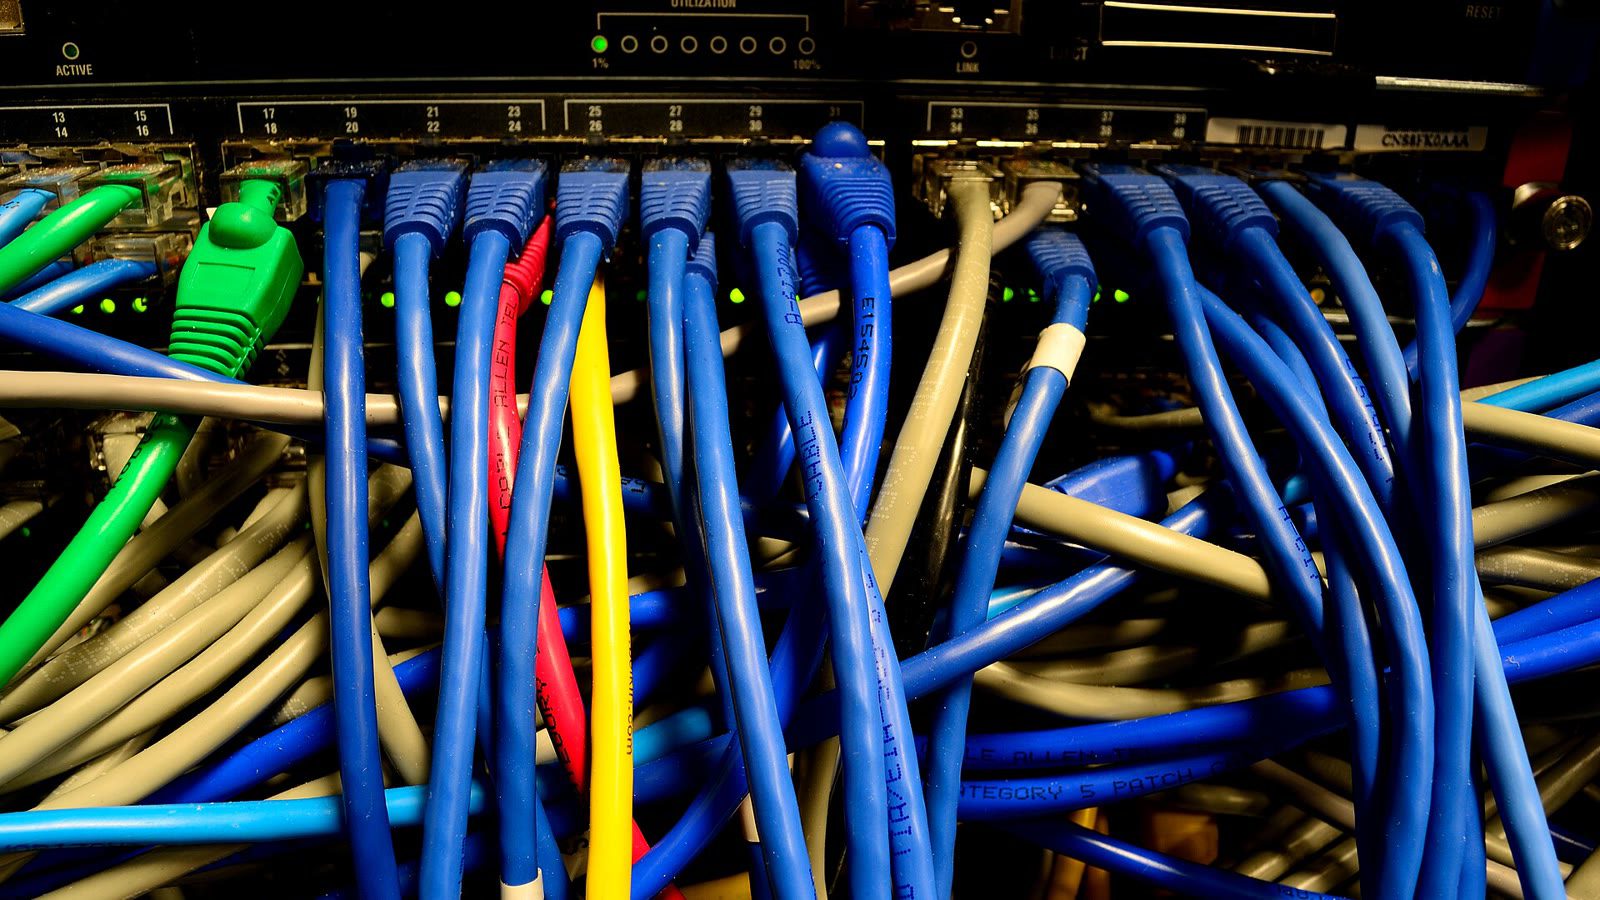
Representative image. Network cables plugged into an Ethernet switch. Photo: Raysonho @ Open Grid Scheduler / Grid Engine / CC0 via Wikimedia Commons
More Stories
 TechnologyConsent manager registration opens under data protection law; ₹2 crore net worth needed
 TechnologySpam call complaints rise 41% to 15.29 lakh in July-September, TRAI data shows
 TechnologyChrome update: CERT-In flags exploited flaw as Google ships 83 more security fixes
 TechnologyCERT-In warns of WordPress flaw under attack; site owners told to update to 7.1.4
 Technology4G saturation project: villages without 4G fall from 45,180 to 11,372 as Centre clears 26,000 more sites
 TechnologySamsung Gallery sync moves to Google storage: 15 GB free, a new ‘Free up space’ option and how to switch it on