Original bilingual journalism · English & తెలుగు
CERT-In names ‘CRAFTY FALCON’ behind attacks on NBFC and fintech payment systems, timed for holidays and weekends
CERT-In's Critical advisory of 4 November says a group it calls CRAFTY FALCON is breaking into the payment and loan-disbursement systems of NBFCs, fintechs, payment firms and crypto exchanges. The advisory deals with the companies' own servers and payment systems; it does not describe attacks on customers' phones.

India’s national cyber security agency, CERT-In, has warned that a hacking group it calls CRAFTY FALCON is breaking into the payment systems of non-banking finance companies (NBFCs), digital lenders, fintech firms, crypto exchanges, payment aggregators and payment service providers. Its advisory CIAD-2026-0058, issued on Wednesday, 4 November, is rated Critical.
The advisory deals with the companies’ own systems: the servers and application programming interfaces (APIs) that pay out loans, settle merchant payments and move money. It does not describe attacks on customers’ phones. CSIRT-Fin, the finance-sector response team under CERT-In, gave the group its name.
CERT-In says the threat has not stopped. Successful break-ins are still being reported, including at NBFCs and fintechs that had received restricted warnings and begun repairs. The same firms were deliberately targeted again, in some cases after an incomplete clean-up. The attackers chose holidays, weekends and quiet hours, when fewer people watch the systems, so that the theft would be spotted late.
How the attackers get in
One way in is a test or staging system left open to the internet. From there the intruders reach live systems through logins or tokens the two share. They take the firms’ apps apart and use altered app packages to call payment APIs directly, getting past checks that trusted only the genuine app to make such calls.
Before a large transfer, they send a tiny payment, as small as Rs 1, to test the route. Payment aggregators’ merchant settlement APIs have been misused, and crypto exchanges have had wallet keys stolen and money siphoned from their wallets. CERT-In says the group uses publicly available automated attack tools that can run a whole attack on their own.
What firms have been told
Firms are told to keep security monitoring running 24×7, with extra staff on holidays and weekends, and to cut test systems off from live ones. Payment monitoring should flag a small transfer to a new beneficiary that is followed by a large one, and stop it for checks. Crypto wallet keys should be kept in cold storage or hardware security modules. The public advisory gives no steps for individual customers.
The note updates CIAD-2026-0046 of 9 October, which described attackers stealing the API credentials firms use with payment gateways and partner banks, then sending money over IMPS and NEFT to mule accounts at several banks. Firms that spot suspicious activity should isolate the affected machines, keep the logs, change every credential and report the incident to CERT-In and CSIRT-Fin. Bulk fraudulent transactions go to the Indian Cybercrime Coordination Centre (I4C).
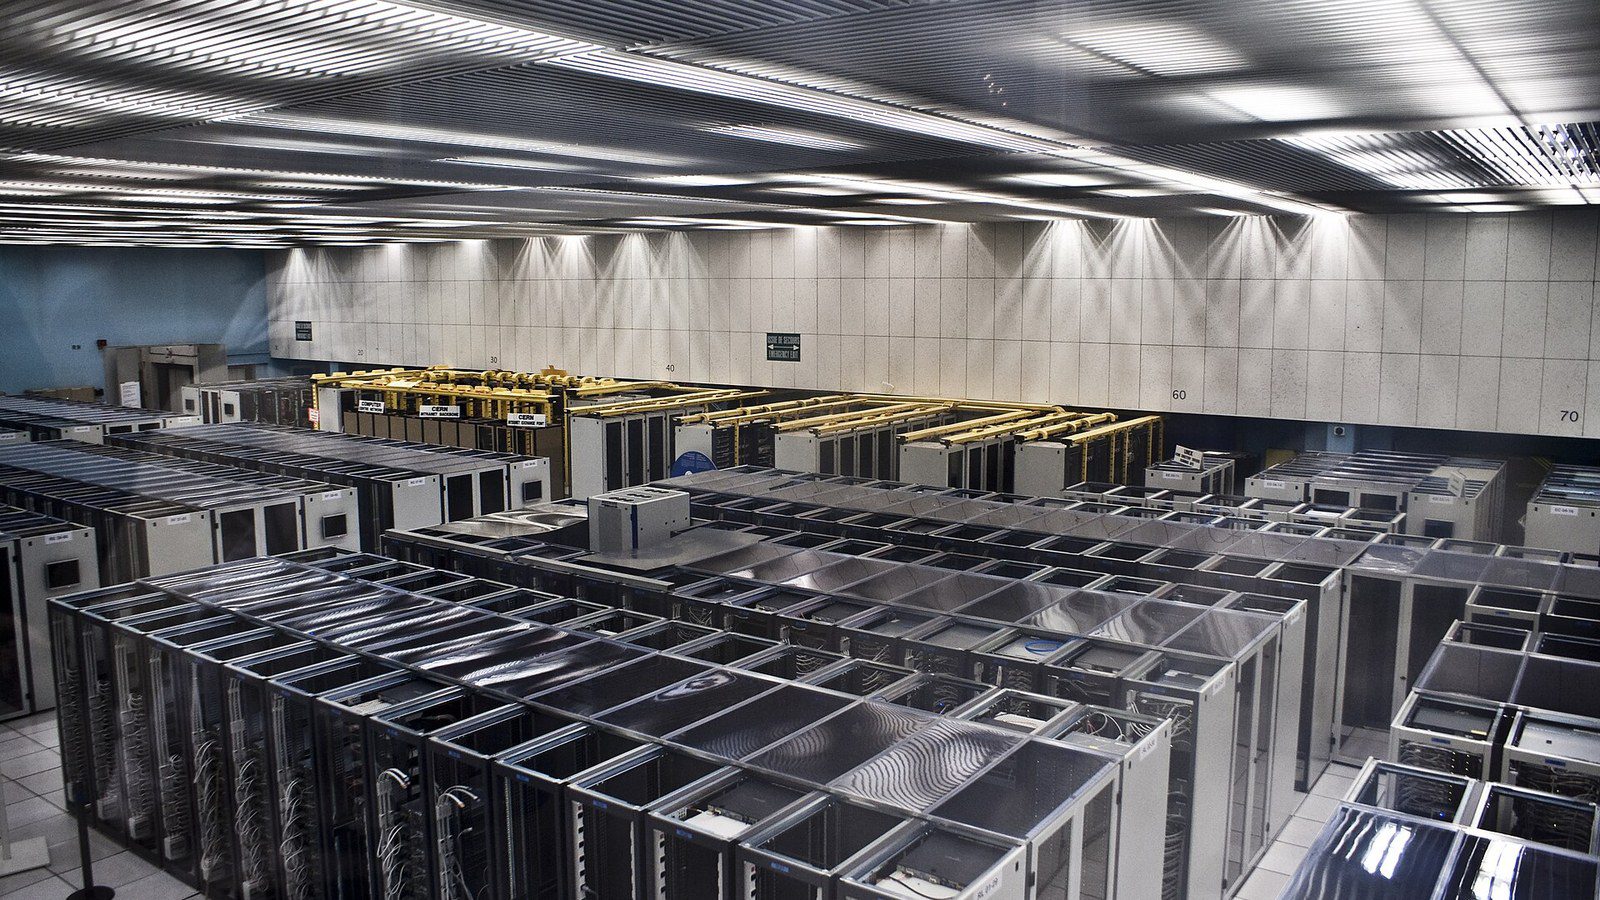
Representative image: server racks in a data centre. Photo: Florian Hirzinger / CC BY-SA 3.0 via Wikimedia Commons
More Stories
 TechnologyAndroid security update: CERT-In rates flaws in Android 14 to 17 critical; how to check your phone’s patch level
 TechnologyStartup India portal links to I-STEM: 31,540 lab instruments at 4,044 institutions, Hyderabad’s CSIR labs among them
 TechnologyDeepavali gift links: Hyderabad police warn of fake Rs 1,000 Paytm offer as TGCSB flags Rs 8,000 ‘PM gift’ message
 TechnologySemicon 2.0 opens for applications as Vaishnaw asks for 18-19 ‘non-serious’ electronics scheme applicants to be rejected
 TechnologyBharatNet in Telangana: Centre signs Rs 3,189 crore pact to take fibre to 12,769 gram panchayats
 TechnologyJailer 2 OTT date: Rajinikanth’s film streams on Prime Video from 12 November, Telugu included