Original bilingual journalism · English & తెలుగు
CERT-In warns of WordPress flaw under attack; site owners told to update to 7.1.4
A flaw in WordPress's own upgrade routine lets attackers run code on a server without logging in. CERT-In says it is being exploited and lists 25 safe releases.

Attackers are exploiting a flaw in the way WordPress updates itself, the Indian Computer Emergency Response Team (CERT-In) said in a vulnerability note issued on Thursday, 12 November. The WordPress vulnerability is present in every core release from 4.7.0 to 7.1.3, and the agency has rated it high severity.
The weakness lies inside the upgrade routine. When a site installs a full new package of the core software, WordPress unpacks the files into temporary folders whose location can be guessed and which are reachable over the web. An intruder who finds that staged installer while the upgrade is under way can interfere with it and run code of their choosing on the server, with no password needed. CERT-In warns that a successful attack can hand over control of the server and expose sensitive data. The flaw is tracked as CVE-2026-119977.
A fix has been available since 28 October
WordPress closed the gap in version 7.1.4, a security release dated 28 October that lists 13 fixes, eight of them for stored cross-site scripting. The project asked owners to update at once and carried the fixes back to every older branch still receiving security patches, as far as 4.7. That is why CERT-In names 25 safe releases, starting at 4.7.39 and ending at 7.0.8 and 7.1.4.
The same release also replaced the bundled root certificates after the revocation of eMudhra certificates. CERT-In had issued a separate advisory on 21 October about the compromise of eMudhra intermediate certificate authority certificates.
In the United States, the Cybersecurity and Infrastructure Security Agency added the upgrade flaw to its catalogue of known exploited vulnerabilities on 3 November and gave federal agencies until 6 November to deal with it.
What site owners need to check
CERT-In addresses its note to all organisations and individuals running WordPress. The version number appears in the site dashboard. A site on 7.1.4, or on the patched release of its own branch such as 6.8.12 or 6.9.11, already carries the fix. An older build needs the patch, which WordPress says can be installed from the Updates screen of the dashboard with the Update Now button. Where automatic background updates are allowed, the release installs itself.
The next major version, WordPress 7.2, is scheduled for 8 December.
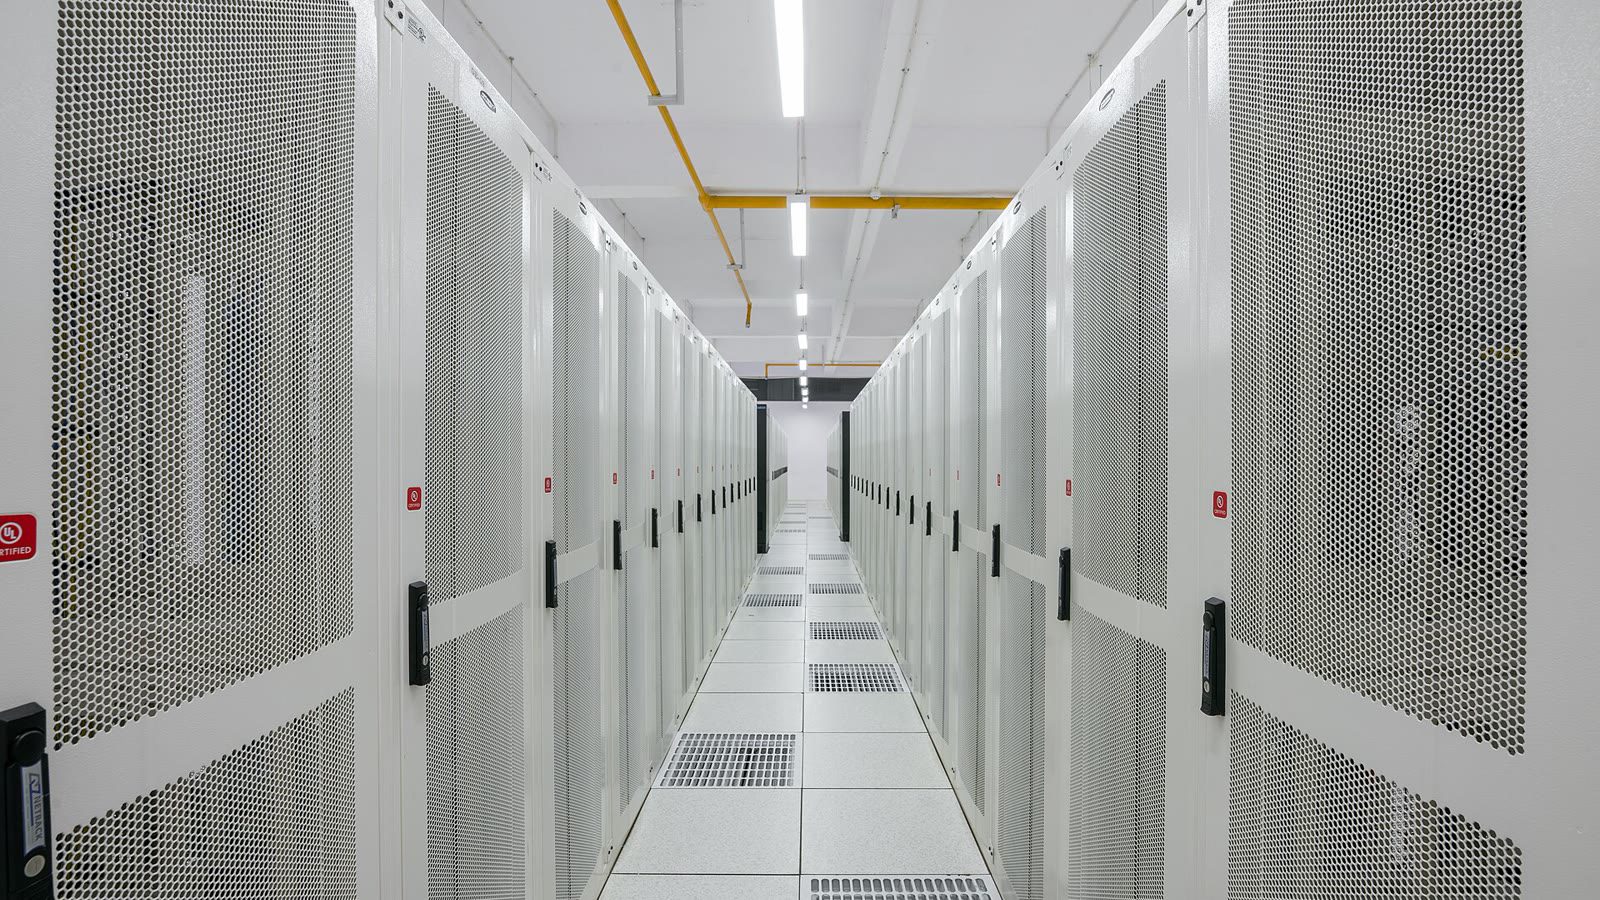
Representative image. Server racks at Pi Data Centers. Photo: PiDatacenters / CC BY-SA 4.0 via Wikimedia Commons
More Stories
 TechnologySpam call complaints rise 41% to 15.29 lakh in July-September, TRAI data shows
 TechnologyChrome update: CERT-In flags exploited flaw as Google ships 83 more security fixes
 Technology4G saturation project: villages without 4G fall from 45,180 to 11,372 as Centre clears 26,000 more sites
 TechnologySamsung Gallery sync moves to Google storage: 15 GB free, a new ‘Free up space’ option and how to switch it on
 TechnologyGemini task automation reaches India: Google’s assistant can book cabs and order food on Pixel 10, Pixel 11 and Galaxy S26 phones
 TechnologyInstagram Teen Accounts: Meta takes age-estimation checks worldwide, moving suspected teens into restricted settings even with an adult birthday